IT Governance & Compliance
We put in place the policies, records and controls that auditors and regulators expect to see.
- Network & Connectivity
- Security & Surveillance
- Connected Healthcare
- Smart Cities & Infrastructure
- Fleet & Logistics
- Energy & Smart Utilities
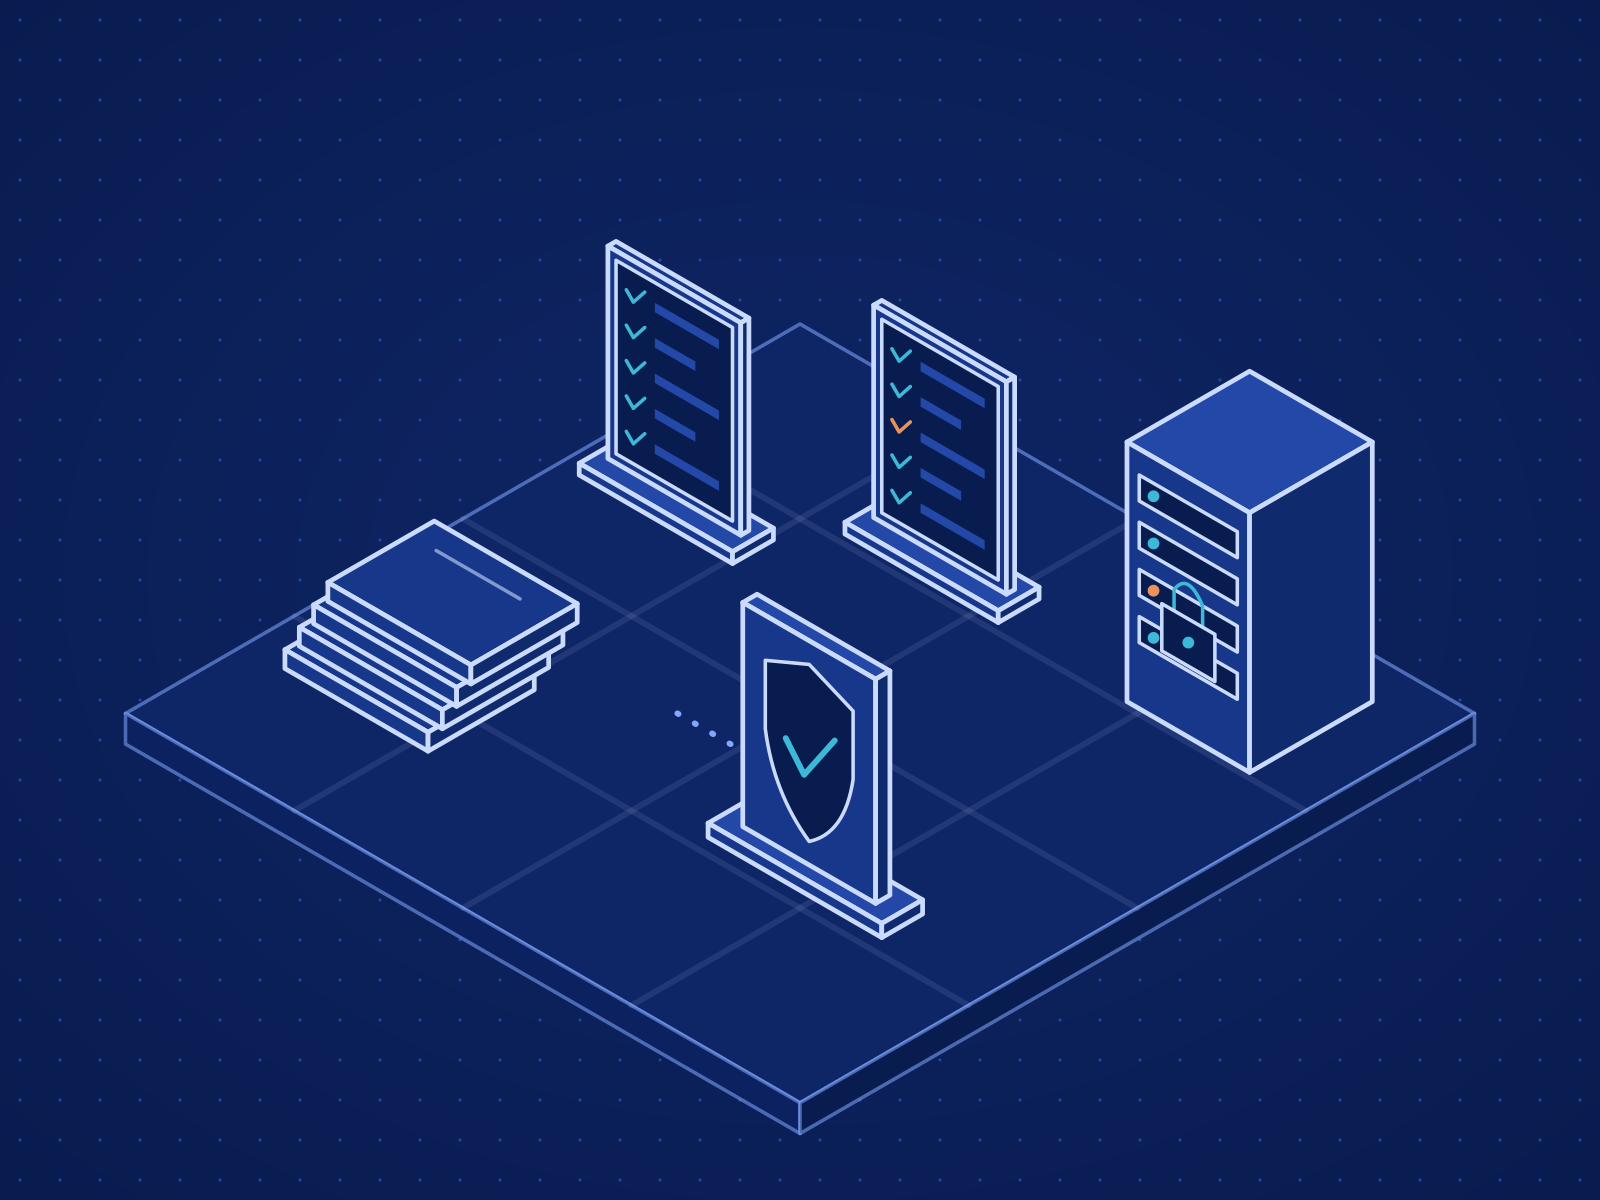
Governance and Audit Support
We prepare organizations for SOC 2, ISO 27001, HIPAA and GDPR audits. The work spans access governance, security reviews, asset inventory, configuration management, policy documents and operational reporting.
Managed IT Services
Each service below can be contracted on its own or combined into a single managed agreement.
Compliance Readiness & Audit Evidence
IT controls mapped to SOC 2, ISO 27001, HIPAA or GDPR, gaps identified, and evidence gathered for your auditors.
IT Asset & Configuration Management
An accurate hardware and software inventory, with configuration baselines enforced and unapproved tools identified.
Security Policy & Procedure Development
Acceptable use, incident response, access control and data retention policies, written and then put into practice.
Vendor Risk Management
A review of each software vendor's security and compliance before it connects to your systems.
vCIO & Long-Range IT Roadmapping
A virtual CIO who plans IT budgets, spending and operations against the goals of the business.
Technologies & Delivery Models
Identity Cloud
The tools we rely on for this layer of the system.
Why KoderTroop for IT Governance & Compliance
Devices, cloud and applications delivered by one partner, with every decision documented and handed over.
Less Downtime
Monitoring, preventive maintenance and fast incident response reduce the time systems are unavailable.
Layered Security
Layered controls, threat hunting and prompt patching lower both the likelihood and the impact of a breach.
Predictable IT Costs
Standard processes and automated administration keep monthly IT costs steady and easy to forecast.
Room to Grow
New staff, offices and cloud services are added onto infrastructure that is already standardized.
Related Case Studies
Frequently Asked Questions
Your IT Governance & Compliance Project
Tell us what you are building and the constraints around it. We will scope the work with you.
Infrastructure & Security Assessment
We review infrastructure, networks, endpoints, cloud services, security and continuity plans, and report the gaps we find.
Onboarding and Hardening
We install monitoring, EDR agents, endpoint management profiles and identity controls, and document the environment as we go.
Day-to-Day Operations
We run monitoring, the helpdesk, infrastructure administration, patching and security operations, and respond to threats.
Optimization & IT Planning (vCIO)
We plan upgrades, security improvements, capacity and hardware refresh, and review them with you each quarter.