How to apply zero-trust architecture to remote edge gateways, AMI networks and industrial control systems with mTLS, hardware TPMs, ephemeral VPN tunnels and read-only root filesystems.
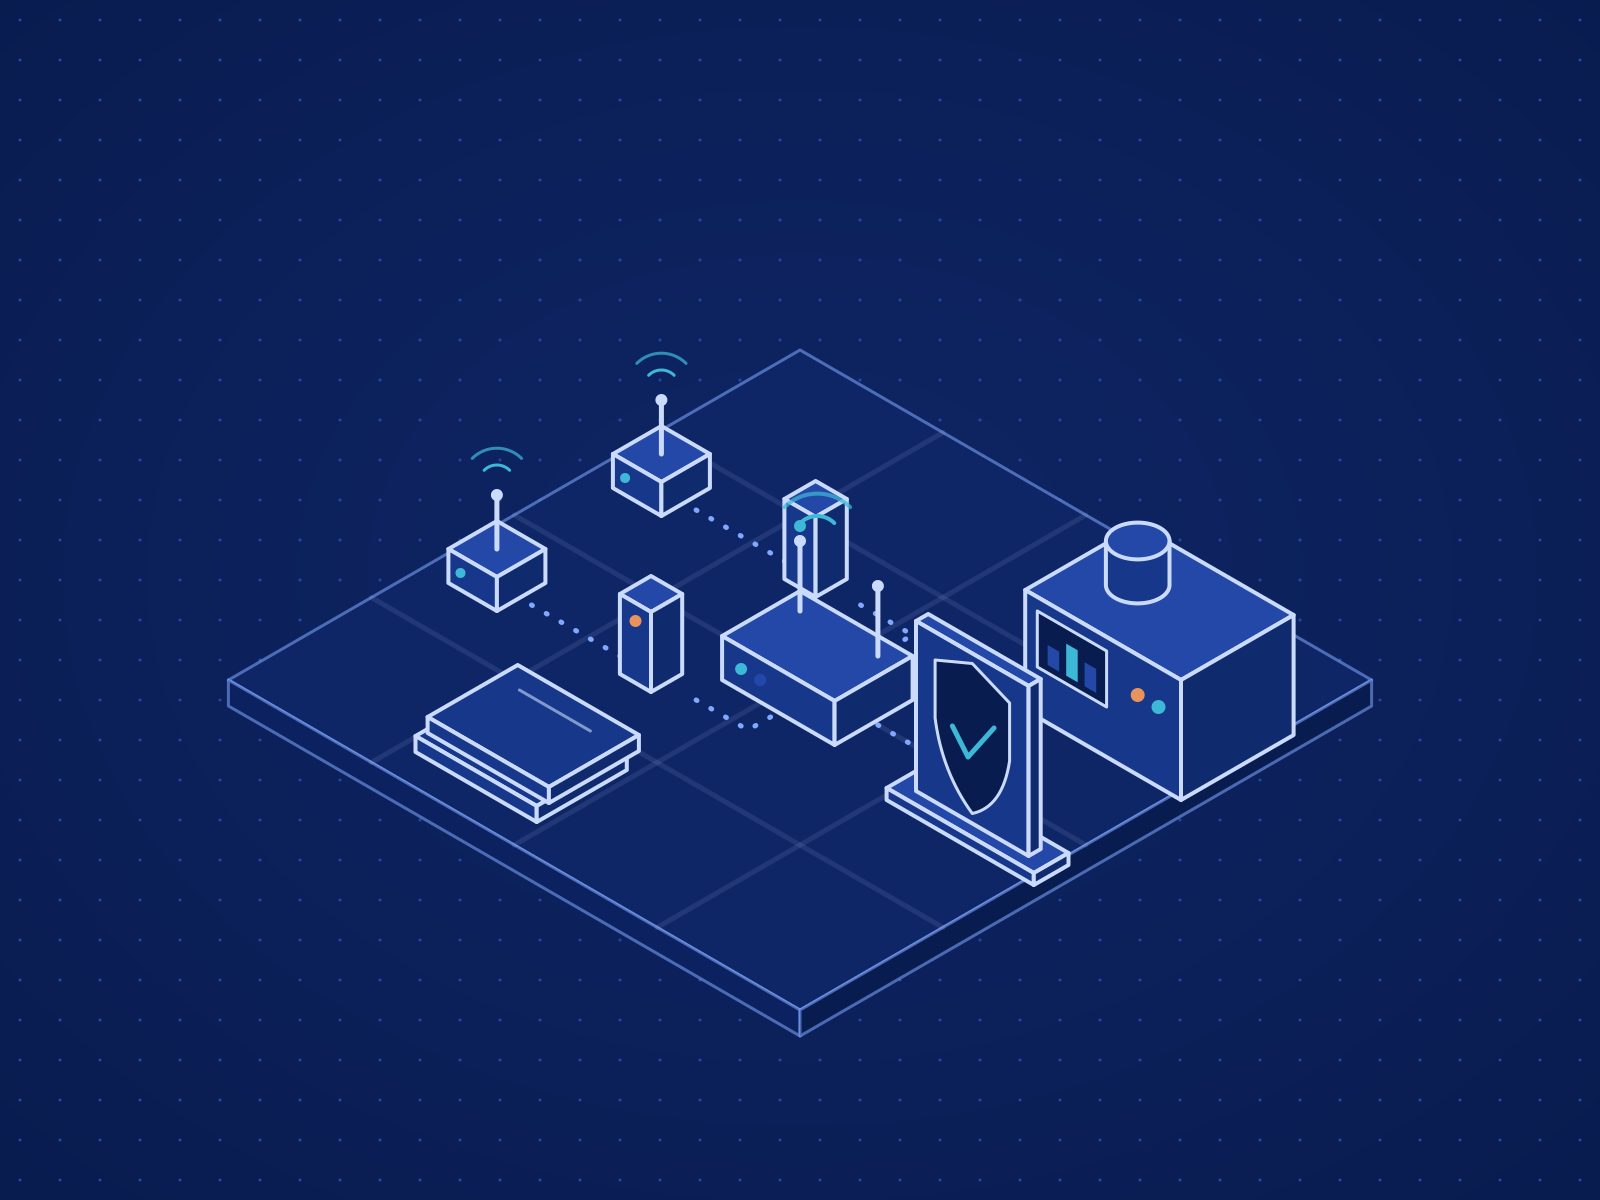
Industrial edge networks cannot borrow the security model of a data center. Their devices are remote, physically reachable and expected to run for years with little attention. Zero-trust IoT and edge security starts from the assumption that any single node can be compromised, and arranges the system so that it does not matter.
The Building Blocks
- Per-device identity anchored in a hardware TPM, so keys cannot simply be copied off the device.
- Mutual TLS on every connection, with no implicit trust based on network location.
- Ephemeral, encrypted VPN tunnels through a CloudLAN mesh overlay.
- Read-only root filesystems with signed, atomic updates that apply completely or not at all.
Meshing Nodes with WireGuard and mTLS
WireGuard provides the encrypted tunnel, and mutual TLS authenticates the services that talk through it. In the configuration below, the device key is provisioned from the TPM, and a keepalive holds the tunnel open through NAT and unreliable links.
[Interface]
PrivateKey = <device-key-from-tpm>
[Peer]
PublicKey  = <hub-key>
AllowedIPs = 10.80.0.0/16
PersistentKeepalive = 25   # survive NAT and flaky links
Layered together, these controls contain a compromised gateway to itself. There are no shared secrets to steal, no flat network to move across and no unsigned code that the device will run.
Tagged Under
KoderTroop Systems Squad
Technical Authors
Articles are written by KoderTroop specialists and architects who design and deliver embedded systems, cloud platforms, edge computing and applied AI for our clients.