Zero trust for overlay networks: cryptographic identity in place of perimeter rules, verified on every request.
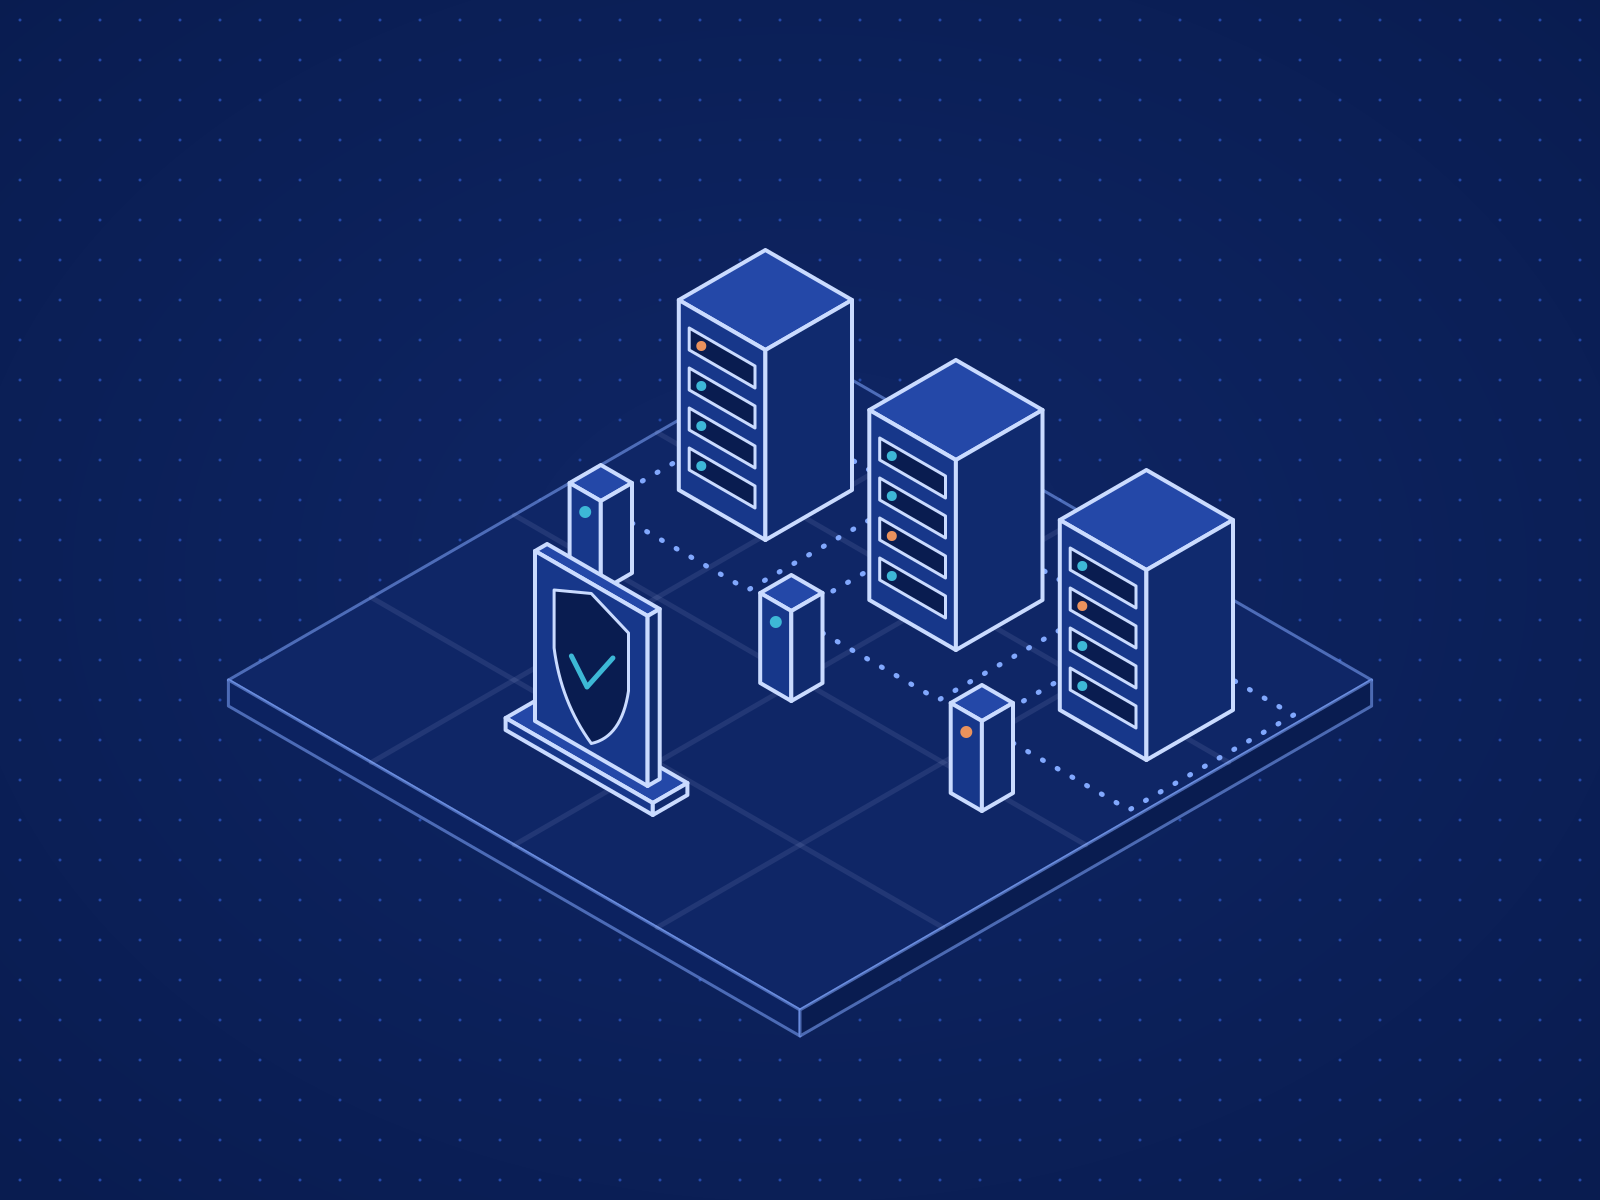
A perimeter firewall assumes there is an inside worth trusting. Multi-cloud estates, remote staff and third-party services have erased that inside. Zero trust replaces the question of where a request comes from with two better ones, who is asking and what they are allowed to do, and answers both on every request.
The Core Principles
- Verify explicitly: authenticate and authorize every request, including traffic between internal services.
- Least privilege: grant the minimum access needed, for the shortest practical time.
- Assume breach: segment the network so one compromised workload cannot reach the rest.
Cryptographic Identity Over IP Addresses
In an overlay network, identity is a key pair rather than an address. Each service presents a short-lived certificate, and its peer verifies it through mutual TLS before any application traffic flows. Policy is written against roles and identities, so moving a workload to another subnet or another cloud changes nothing about what it may reach.
[peer]
auth     = mtls
cert_ttl = 3600          # short-lived, auto-rotated
allow    = role:payments  # authorize by identity, not subnet
deny     = *
Operationally, access changes become certificate operations. Onboarding a node means issuing a certificate; revoking a compromised one means withdrawing it. No firewall rules need migrating, and an attacker who lands on one workload finds that the next segment does not recognize them.
Tagged Under
KoderTroop Systems Squad
Technical Authors
Articles are written by KoderTroop specialists and architects who design and deliver embedded systems, cloud platforms, edge computing and applied AI for our clients.