DevSecOps & Platform Automation
We automate build, test, security scanning and deployment, so every release passes the same checks and none depends on one person's memory.
- Network & Connectivity
- Security & Surveillance
- Connected Healthcare
- Smart Cities & Infrastructure
- Fleet & Logistics
- Energy & Smart Utilities
DevSecOps & Platform Automation
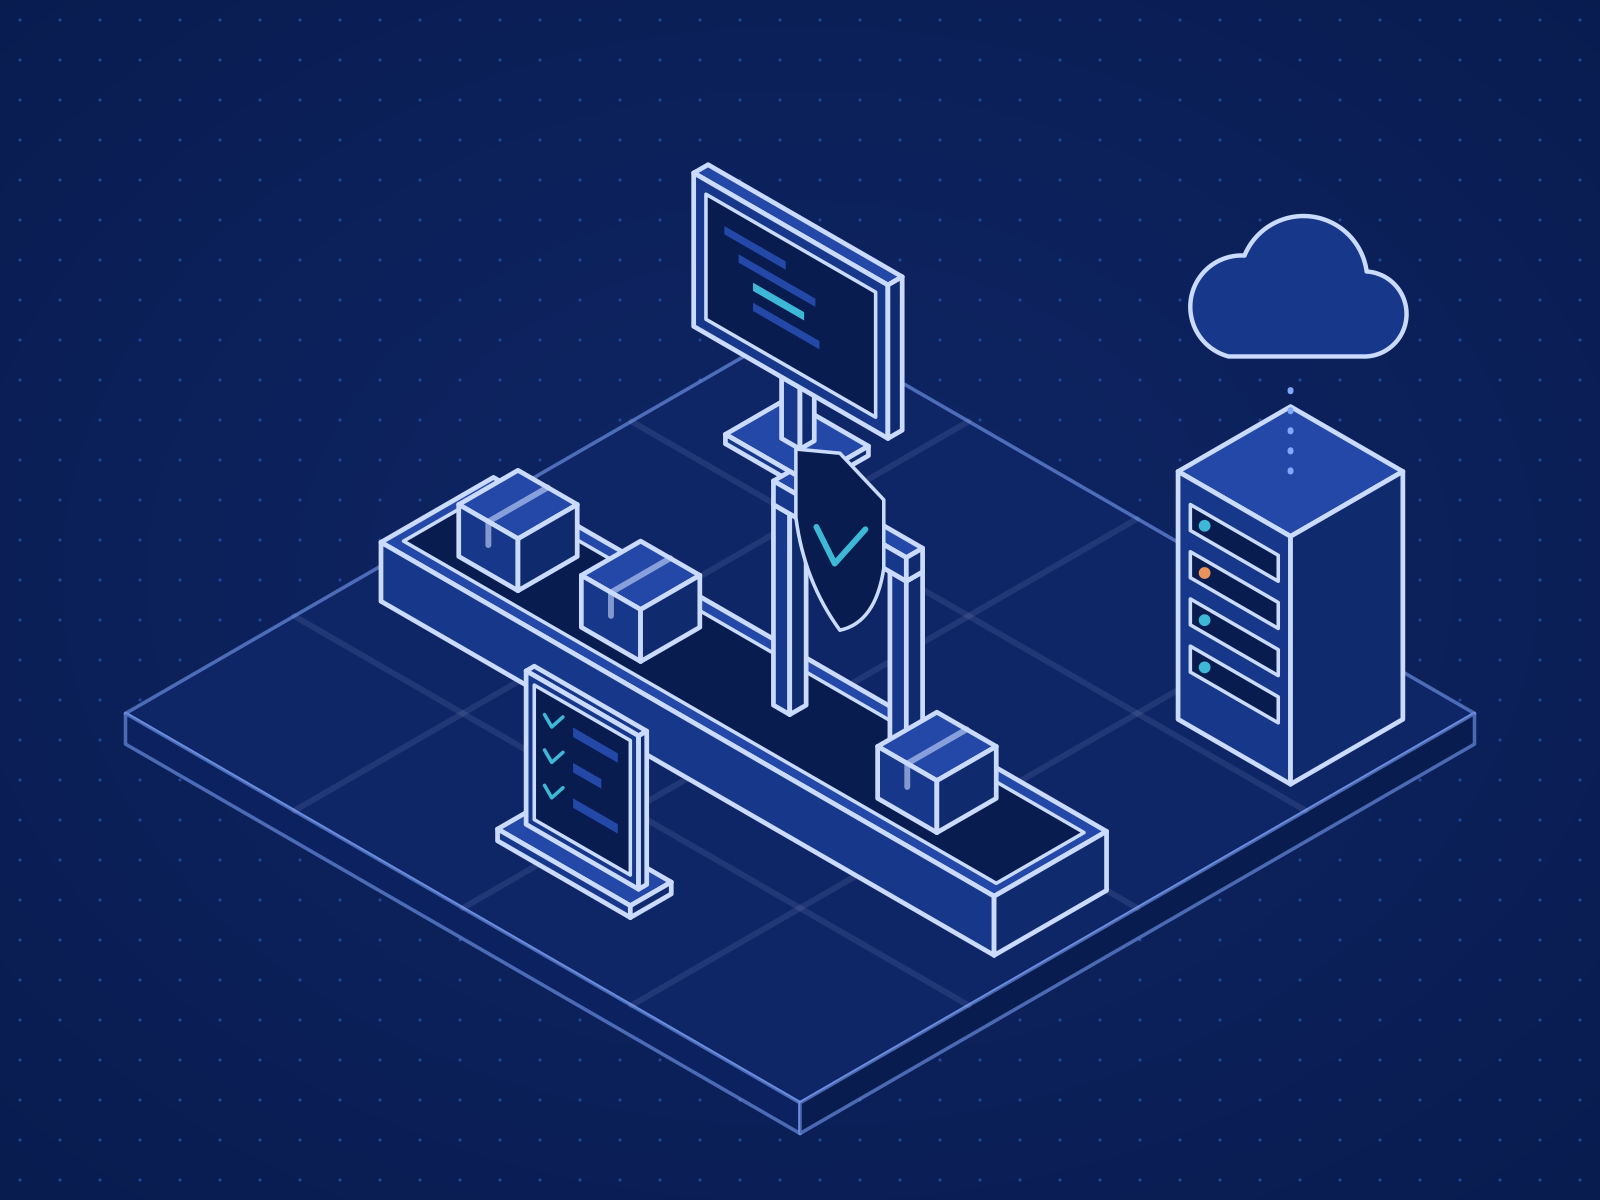
We set up build pipelines, infrastructure provisioning, container orchestration, security scanning, monitoring and release automation. Where SOC 2, HIPAA or PCI DSS controls apply, we encode them in the pipeline as automated checks, so the evidence builds up with every release.
Web, Mobile and Cloud Services
Each service below can be engaged on its own or combined into a single platform build.
Continuous Integration & Delivery (CI/CD)
Automated build, test and deployment in GitHub Actions, GitLab CI or Jenkins, replacing manual release steps.
Automated Security Scanning
Static (SAST), dynamic (DAST) and dependency scans that run in the pipeline on every change.
Observability & Application Monitoring
Central logging, distributed tracing and alerting in Prometheus, Grafana, Datadog or the ELK stack.
Release Management & Feature Flags
Blue/green and canary releases behind feature flags, so new code reaches production without downtime.
Secrets & Configuration Management
API keys, database credentials and environment settings held in HashiCorp Vault, AWS Secrets Manager or Azure Key Vault.
Technologies & Delivery Models
Frontend Mobile
The tools we rely on for this layer of the system.
Why KoderTroop for DevSecOps & Platform Automation
Devices, cloud and applications delivered by one partner, with every decision documented and handed over.
Capacity That Scales
Services run in containers with autoscaling rules, so peak demand needs no manual intervention.
Automated Releases
CI/CD pipelines and infrastructure as code make every release repeatable and quick to reverse.
Security in the Pipeline
Vulnerability scanning in CI/CD, central identity management and least-privilege access are in place from the first build.
Room for the Next Feature
Modular services make it straightforward to add features, AI capabilities or new device types later.
Frequently Asked Questions
Your DevSecOps & Platform Automation Project
Tell us what you are building and the constraints around it. We will scope the work with you.
Architecture & Technical Discovery
Requirements become an architecture, cloud plan, API contracts, security model and phased delivery plan.
Platform Development
We build the frontend, backend services, APIs, cloud infrastructure and deployment pipelines in short iterations.
Testing and Review
Automated tests and peer review check function, performance, security and accessibility on every change.
Deployment & Cloud Operations
We release through automated pipelines, then monitor application health, security and cost after launch.